Law Smith
Founder & President, Tocobaga
Law Smith is the Founder and President of Tocobaga, a Tampa-based ROI-focused marketing agency and SMB advisory. He has strategically advised 1,000+ small and medium businesses, executed 600+ integrated marketing campaigns, and written 30+ business plans across industries ranging from professional services to e-commerce to B2B technology. Tocobaga is a Google Partner and Squarespace Gold Partner headquartered in Ybor City.
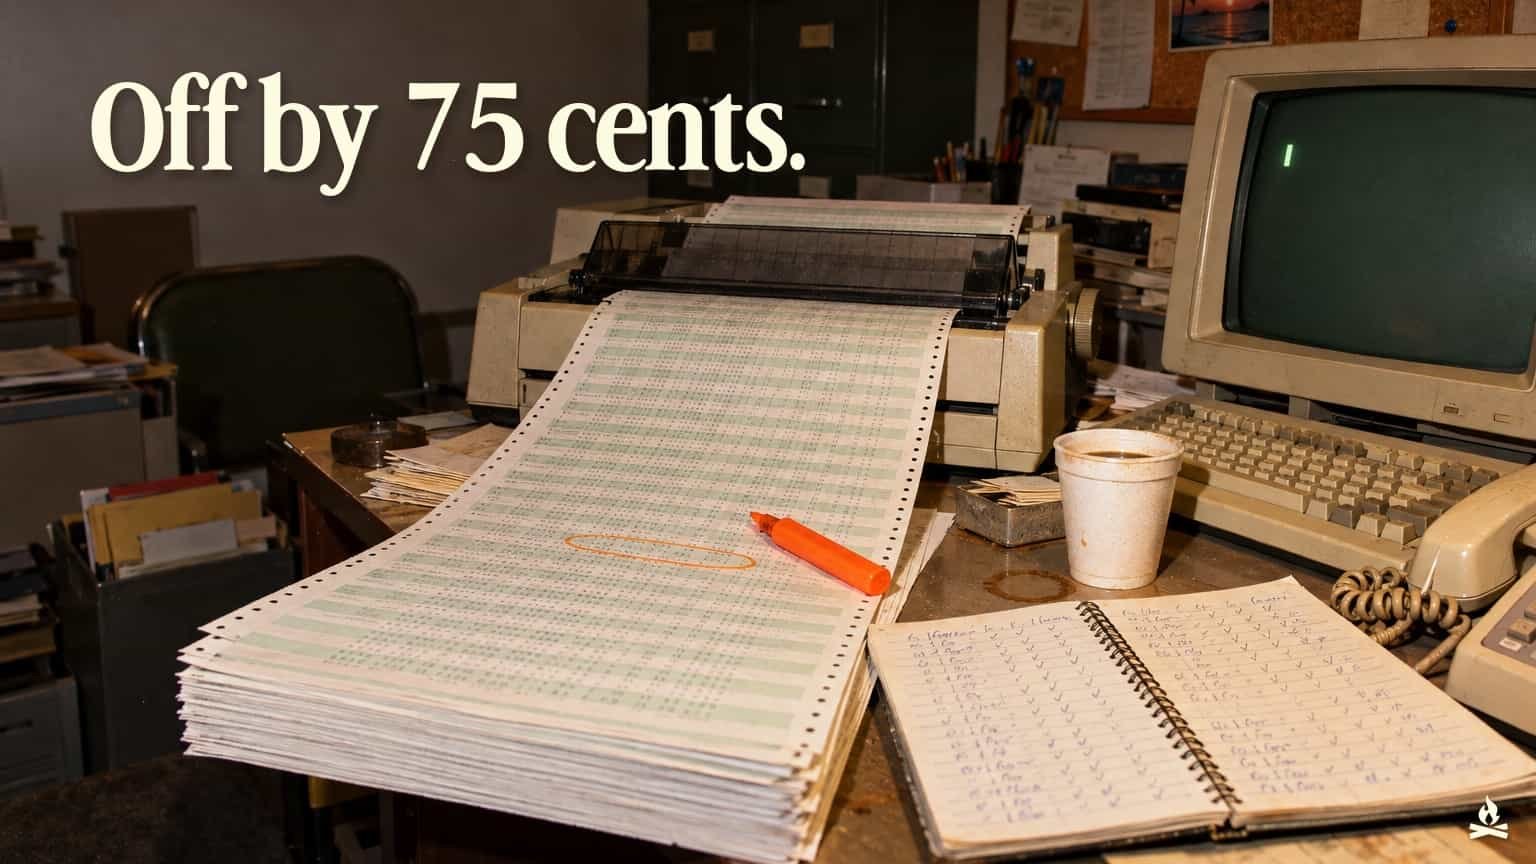
In August 1986, Clifford Stoll was an astronomer working a job that had nothing to do with stars. He managed computers at Lawrence Berkeley Laboratory in California, and his supervisor handed him a chore that bordered on insulting: the lab's computer usage accounts were off by 75 cents.*,† Somebody had burned nine seconds of machine time without paying for it.† Nine seconds. Three quarters. A rounding error in a building full of physicists.
Stoll did not round it down. He traced the nine seconds to an account nobody had authorized and, instead of deleting it, he watched it. He attached teleprinters to the incoming lines so every keystroke the visitor typed landed on paper.†,* He kept a logbook of every session, every trace and every call to law enforcement.*
The visitor attacked about 450 computers over roughly ten months, many of them on military networks, and got into more than 30.* He did not need genius. Roughly one in 50 machines he tried still had an account named FIELD with the password SERVICE.‡ When Stoll called the FBI, the bureau said it would not engage unless classified information was stolen or more than half a million dollars in computer resources went missing.‡ Seventy-five cents did not clear the bar.
So Stoll and his partner, Martha Matthews, then a Berkeley law student, built a trap: a phony SDInet folder stuffed with impressive-sounding bureaucratic files about a fictitious missile-defense project.‡,† The intruder stayed online long enough for the Deutsche Bundespost to trace him to his home in Hanover, West Germany.† Markus Hess and two accomplices had been selling what they found to the KGB, for about 30,000 Deutschmarks by one account, and a West German court convicted them of espionage on February 15, 1990.§ Stoll's later paper put the moral in two sentences: "From the intruder's viewpoint, almost everyone except LBL detected his activity. In reality, almost nobody except LBL detected him."*
That is the whole problem with small business cybersecurity in 2026. The doors are the same doors: default passwords, unpatched systems, nobody reading the log. What changed is the payout. The FBI's Internet Crime Complaint Center logged $20.877 billion in reported losses in 2025, and business email compromise alone took $3,046,598,558.‖ That is not a Cold War spy novel. That is a Tuesday afternoon invoice.
Tocobaga, the ROI-focused marketing agency and SMB advisory behind SolvingHow.com, headquartered in Ybor City, Tampa, is not an IT security firm, and founder Law Smith says so before anyone asks. But Tocobaga builds websites, manages domains and email platforms, and runs ad accounts for a living, and after advising more than 1,000 small and mid-sized businesses, the pattern is plain: the business that gets hurt is rarely the one that bought the wrong tool. It is the one that ignored its 75 cents. Owners ask the question in their own words on Reddit and across Tampa conference tables: what basic cybersecurity steps are other small businesses actually doing, not enterprise-level stuff, that have prevented problems or bought some peace of mind? Tocobaga's answer is a short list ranked by what stops real losses, priced for a 12-person firm and checked against the losses that actually show up in FBI and insurance claim data.
What should be on a small business cybersecurity checklist?
A small business cybersecurity checklist should be ranked by what causes losses, not by what vendors sell, and the top of that list is a phone call: a rule that nobody changes payment details without calling back a known number. After that come multi-factor authentication on every account, a password manager, fast patching of internet-facing devices, endpoint detection and response, immutable backups that get tested, a vendor access review, email authentication and an incident plan printed on paper.
The order comes from the evidence. The FBI's 2025 data puts business email compromise at roughly $3.05 billion in losses, a crime that needs no malware at all.‖ Verizon's 2026 Data Breach Investigations Report, built on more than 22,000 confirmed breaches, found that exploiting a software vulnerability became the top way into a breach at 31 percent, while credential abuse fell to 13 percent, and ransomware showed up in 48 percent of breaches.¶ Where the victim's size was known, about 96 percent of ransomware victims were small and midsize businesses.¶ The crooks are not hunting whales. They are trawling.
The checklist, in the order Tocobaga would fund it:
A call-back rule: no change to bank details, wiring instructions or payees without a call to a number already on file, plus a second approver above a set dollar amount.
MFA on every account that touches money, identity or customers, with hardware keys or passkeys for the people who approve payments.
A business password manager, so every password is long, unique and revocable in one click when someone leaves.
A patch window for firewalls, VPNs and remote-access tools measured in days, plus replacement of anything the manufacturer no longer supports.
Endpoint detection and response on every laptop and server, with a named human who reads the alerts.
Backups with at least one immutable copy, kept outside the normal logins and restored in a timed test every quarter.
A vendor access list showing who has remote access, admin rights or payment authority, reviewed every quarter and after every acquisition.
SPF, DKIM and DMARC on every domain the company sends from, with DMARC moving toward enforcement.
A one-page incident plan on paper with the bank's fraud line, the insurer's hotline, the IT provider and outside counsel.
Employee habits from the federal floor: report phishing, use long unique passwords, turn on MFA and install updates.
That last line is not filler. CISA's Secure Our World campaign boils the basics down to four habits: recognize and report phishing, use passwords of at least 16 characters that are random and unique, turn on multifactor authentication, and update software.** What is missing from the whole list is telling: an AI-powered anything, a five-figure monitoring contract, a dashboard with a world map of blinking attacks. Clifford Stoll caught a KGB asset with borrowed printers and a notebook. The expensive part of security is attention, and attention is cheap only when it is organized.
| Control | What it stops | Rough monthly cost, 12 people | Evidence |
|---|---|---|---|
| Call-back rule for payment changes | Wire fraud and business email compromise | $0 | BEC losses of $3.05 billion in 2025 (FBI IC3, 2026) |
| MFA everywhere, keys for money movers | Account takeover from stolen passwords | About $5 for hardware keys | MFA stops 99.9% of credential attacks (Microsoft via ABA, 2023) |
| Business password manager | Reused and shared passwords, messy offboarding | $48 to $96 | Passwords of 16+ random, unique characters (CISA, 2024) |
| Patch firewalls, VPNs and remote access | Exploited vulnerabilities, now the top entry point | Part of IT provider time | Exploitation in 31% of breaches (Verizon DBIR, 2026) |
| EDR with a named reader | Ransomware spreading across devices | $96 to $264 via Microsoft 365 Premium | Premium held at $22 per user (Nerdio, 2026) |
| Immutable, tested backups | Ransom payments and long downtime | About $150 (assumption) | Average ransomware claim of $269,000 (Coalition, 2026) |
| Vendor access review | Breaches through IT providers and suppliers | $0 plus a quarterly hour | Third parties in 48% of breaches (Verizon DBIR, 2026) |
| SPF, DKIM and DMARC | Domain spoofing and spam-foldered marketing | $0 to a modest setup fee | Required for Gmail bulk senders (Google, 2024) |
| Paper incident plan | Lost hours, voided coverage, unrecovered wires | $0 | 58% of attempted theft frozen when reported (FBI IC3, 2026) |
How do small businesses prevent business email compromise?
Small businesses prevent business email compromise with a rule, not a product: no one changes bank details, wiring instructions or a vendor's payment account based on an email, text or call alone, and every change gets a call-back to a phone number already on file. Above a set dollar amount, a second person approves the change before any money moves.
The scale justifies the bureaucracy. The FBI received 24,768 business email compromise complaints in 2025 carrying $3,046,598,558 in losses, which works out to about $123,000 per complaint.‖ Coalition, a cyber insurer that publishes its claims data every year, found that business email compromise and funds transfer fraud together made up 58 percent of the incidents it saw in 2025; funds transfer fraud averaged a $141,000 loss, and 52 percent of those cases started with a compromised mailbox.†† For a business running a 15 percent net margin, one $141,000 wire to a stranger means booking about $940,000 in new revenue just to get back to even.
The scenario is easy to picture. A three-attorney real estate practice in Brandon has a $412,000 closing set for Friday. On Thursday afternoon an email arrives from the title agent's real address, because her account was quietly compromised three weeks earlier, with "updated" wiring instructions and a polite note that the old account is under audit. The thread is genuine. The signature is genuine. The bank is new. A paralegal trained on a call-back rule ignores the phone number in the email signature, pulls the number from the engagement file and dials. The agent never sent anything. Total cost of the control: four minutes.
When the rule fails, speed is the only asset left. The FBI's Recovery Asset Team, through its Financial Fraud Kill Chain, froze $679,013,183 of $1,163,919,846 in attempted theft in 2025, a 58 percent success rate across 3,900 incidents.‖ The order matters: the bank's fraud line first, then a report to IC3, then the insurer. In a business email compromise, the 75 cents is a new bank in a different state, a sudden "quick favor," a Friday deadline. The alarm is always small. The logbook is a vendor master file with phone numbers no email can edit.
Is multi-factor authentication enough to stop account takeovers?
Multi-factor authentication stops the large majority of password-based account takeovers, but it is not enough on its own in 2026, because attackers now steal logged-in sessions and spam approval prompts until a tired employee taps yes. MFA has to cover every account without exception, and the people who move money or hold admin rights should use phishing-resistant methods such as hardware security keys or passkeys.
The case for MFA is not close. The American Bar Association's 2023 Cybersecurity TechReport cited Microsoft data showing that MFA stops 99.9 percent of credential-based account attacks, yet only 54 percent of attorneys said two-factor authentication was even available at their firms.‡‡ That gap is not a law firm quirk. SpyCloud's summary of Verizon's 2026 report noted that 37 percent of organizations had an administrator account with MFA disabled on a cloud infrastructure service.§§ An attacker does not need every door open. One will do.
MFA fails in three predictable ways. The first is coverage: it protects the email login but not the domain registrar, the payroll portal or the Google Ads account, and the crook walks in through the side door. The second is fatigue: push notifications that a distracted employee approves to make the buzzing stop, which is why number matching and a standing rule of "never approve a prompt nobody started" matter. The third is theft of the session itself, where malware copies the browser cookie that proves the login already happened, a problem that infostealer malware has turned into an industry.
The practical order of operations starts with the accounts that touch money or identity: email administrators, banking, payroll, the domain registrar and DNS host, the website, and every ad platform. Everything else follows. Hardware keys for the two or three people who approve payments cost about as much as a nice dinner and remove the possibility of a phished code. In Stoll's 1986 hunt, he reported that a dictionary attack could crack about 20 percent of the Berkeley lab's user passwords.* A second factor would have made most of those passwords worthless.
Does a small business really need a password manager?
Yes. A business password manager is the only practical way for a team to follow CISA's guidance of passwords that are at least 16 characters, random and unique to every account, and it gives the owner a single list of who has access to what.** For most small firms it costs less per month than the office coffee.
The pricing is not a hurdle. 1Password Business runs $7.99 per user per month on an annual plan, and Bitwarden's Teams plan runs $4 per user per month.‖‖ For a 12-person firm, that is $95.88 or $48 a month. The alternative is a spreadsheet named "passwords_FINAL_v3" on a shared drive, or twelve people reusing the dog's name across the bank, the CRM and a fantasy football site that got breached years ago.
The quiet benefit is offboarding. When an employee leaves, the shared vaults that person could see are revoked in one click, and the owner knows exactly which shared credentials need rotating. Without a manager, a departing account manager walks out knowing the Meta Business login, the Shopify admin password and the router's admin page, and nobody can say for certain which ones. That is a business-continuity problem wearing an IT costume.
A password manager also becomes the company's access logbook. Every shared credential has an owner, a date and a list of who can see it. Clifford Stoll's real weapon was never the printers; it was the record. A password vault, set up correctly, is the small business version of his notebook: boring, complete and searchable at 2 a.m. when something looks wrong.
How do hackers steal passwords without phishing anyone?
Increasingly, hackers steal passwords and logged-in sessions with infostealers, malware that quietly copies saved passwords, browser cookies and session tokens from an infected computer and ships them to criminal marketplaces. A stolen session can let an attacker skip both the password and the MFA prompt, because the website believes the login already happened.
The link to ransomware is direct. SpyCloud's reading of Verizon's 2026 data found that 73 percent of ransomware victims had an infostealer infection or a credential leak in the year before the attack, and half of those events landed within 95 days of it.§§ Small organizations logged a median of seven credential leak events a year.§§ Seven leaked logins is not a breach yet. It is seven 75-cent discrepancies, waiting for somebody to notice.
A Shopify brand doing $4 million a year shows how it plays out. The marketing coordinator works from a personal laptop at night and installs a free, cracked video-editing plug-in to finish a holiday ad. The plug-in carries an infostealer. Within a week, someone in another time zone holds her logged-in Meta Business session, adds a new admin and starts running ads for a crypto scheme on the brand's stored card at, say, $3,000 a day over a long weekend. Nobody's password was phished. MFA never fired. The first alarm is a credit card statement, and by then the brand has also lost its best-performing ad account to a policy ban.
The defenses are mostly policy. Admin access to stores, ad accounts, banking and email should happen only on company-managed devices with endpoint protection. Browsers should not store business passwords; the password manager should. Owners should know how to revoke all active sessions in Google Workspace, Microsoft 365, Shopify and Meta, because changing a password does not always kill a stolen session. And every ad and commerce account should carry at least two owner-level admins, so a hijacked admin cannot lock everyone else out. For a marketing agency like Tocobaga, that second owner-level admin is a non-negotiable line in every account setup.
Why are firewalls and VPNs now the top way hackers get in?
Firewalls, VPN gateways and remote-access portals are now a leading way in because they face the open internet, run complex code and often go months without updates. Verizon's 2026 Data Breach Investigations Report found that exploiting a vulnerability became the most common initial access route at 31 percent of breaches, and it tied the shift to the growing number of exposed internet-facing systems.¶
Patching is losing the race. Only 26 percent of critical flaws on CISA's Known Exploited Vulnerabilities list were fully fixed in 2025, down from 38 percent, and the median time to remediate rose from 32 days to 43.¶,¶¶ Sophos found the same pattern in its 2025 survey of U.S. organizations with 100 to 5,000 employees: exploited vulnerabilities were the leading technical root cause of ransomware attacks at 27 percent, ahead of phishing at 26 percent and compromised credentials at 23 percent.*** A known-exploited flaw is a public invitation, and 43 days is a long time to leave a door marked "open" on the internet.
Here is the manufacturing version. A family-owned injection molder with 70 employees runs an on-premises ERP system. A contractor installed the VPN appliance in 2021 and moved on. The firmware is 14 months old. The manufacturer publishes a critical fix on a Tuesday; scanners find the unpatched box by the weekend. Sunday night, the ERP server encrypts. Monday morning, the plant cannot print a work order, a pick ticket or a shipping label, and the production manager is running three shifts off clipboards and memory. The ransom note is not the expensive part. The idle press line is.
The fix is an inventory and a calendar. The inventory lists every device that faces the internet: the firewall, the VPN, any remote-desktop gateway, the camera system, the phone system, the old storage box somebody exposed for convenience. The calendar holds automatic updates where the vendor supports them, a subscription to each vendor's security advisories, and a written patch window for critical fixes measured in days, not quarters. Anything past end-of-life gets replaced. In 1986, the default account named FIELD with the password SERVICE opened roughly one in 50 machines the intruder tried.‡ The 2026 version of FIELD and SERVICE is a VPN appliance nobody has logged into since the contractor left.
What is EDR, and does a 12-person company need it?
Endpoint detection and response, or EDR, is security software on every laptop and server that watches behavior instead of just matching known viruses, so it can flag a program that suddenly starts encrypting thousands of files and cut that machine off from the network automatically. A 12-person company needs it, and many already own part of it: Microsoft 365 Business Premium bundles Defender for Business with Intune device management, Entra ID P1 and conditional access.†††
The pricing math is friendlier than most owners assume. When Microsoft raised Microsoft 365 prices on July 1, 2026, Business Basic went from $6 to $7 per user per month and Business Standard from $12.50 to $14, while Business Premium stayed at $22.††† For a firm already on Standard, the upgrade to Premium now costs $8 per user per month. For 12 people, that is $96 a month for EDR, device management and conditional access rules, such as blocking sign-ins from countries where the firm does no business.
The catch is that EDR is a smoke detector, not a fire department. Somebody has to read the alerts, and somebody has to know what "isolate device" means before 2 a.m. on a holiday weekend. IBM's 2025 Cost of a Data Breach study put the average time to identify and contain a breach at 241 days, the lowest in nine years and still most of a year.‡‡‡ Clifford Stoll's fifty borrowed teleprinters would have caught nothing if he had stacked the printouts in a closet. The control is the machine plus the reader.
For firms without a full-time IT person, the reader is usually the managed service provider, and the contract should say so in plain terms: who watches the console, how fast they respond, and whom they call. If the answer is "we get an email," that is a mailbox, not a monitoring service.
How should a small business back up data to survive ransomware?
A small business should keep at least one backup copy that cannot be altered or deleted for a set period, known as immutable storage, held outside the company's normal logins, and it should restore from that copy in a timed test every quarter. A backup that has never been restored is a theory, and ransomware crews go after backups first.
The stakes are concrete. Ransomware appeared in 48 percent of the breaches Verizon analyzed for its 2026 report, up from 44 percent; the median ransom paid was $139,875, down from $150,000, and 69 percent of victims refused to pay at all.¶¶,§§ Coalition's claims data shows why refusing is easier with working backups: ransomware was its costliest claim type in 2025 at an average loss of $269,000, initial demands jumped 47 percent, and a record 86 percent of its policyholders declined to pay.†† The firms that can say no are the ones holding a clean copy.
Backups fail quietly. In Sophos's 2025 survey of U.S. organizations with 100 to 5,000 employees, only 43 percent used backups to recover encrypted data, down from 61 percent the year before, even as 51 percent fully recovered within a week.*** The usual reasons are mundane: the backup lived on a storage device joined to the same Windows domain and was encrypted with everything else, or the backup job ran nightly for two years and nobody noticed it had stopped in March.
Back at the injection molder with the encrypted ERP, the backups decide the week. If its only copy sat on a network drive the attackers could reach, the plant negotiates. If it kept an immutable cloud copy, restored the ERP database to a spare server last quarter and wrote down that the restore took nine hours, the plant loses a shift and a weekend, not a quarter. That written restore time is a logbook entry, and it is worth more than any vendor's promise of enterprise-grade resilience.
The practical rules start with the old 3-2-1 idea: three copies, two kinds of storage, one offsite, with the offsite copy made immutable. The backup system gets separate credentials protected by MFA, so a stolen domain admin account cannot delete it. Cloud data needs its own backup, because Microsoft 365 and Google Workspace retention settings are not the same as a restorable copy. And the test is a restore, not a green checkmark on a dashboard.
How risky are vendors and IT providers to a small business?
Vendors are now one of the biggest risks a small business carries, because every IT provider, bookkeeper, payroll service and marketing agency with a login is another door. Verizon's 2026 report found a third party was involved in 48 percent of breaches, up from 30 percent a year earlier, and breaches tied to the supply chain rose 60 percent.¶,¶¶
For a small business, the third parties are not abstract. The managed IT provider holds remote access to every machine. The outsourced bookkeeper can add payees. The web developer has the hosting password. The marketing agency, Tocobaga included, may hold admin rights to the ad accounts and the website. Each one is a convenience and a liability, and the question is not whether to use vendors but whether the business keeps a current list of who can touch what.
Acquisitions multiply the problem. A PE-backed HVAC platform closing its third add-on, a 25-truck shop with a strong brand and a weak back office, inherits a familiar mess. The founder's nephew ran IT. Every office PC carries the same remote-access tool with a shared password. The office manager approves vendor bank changes by email. The domain has no DMARC record. Four people share one QuickBooks login. On day one of ownership, the platform owns all of it, and an acquisition announcement is public information: a change in ownership is exactly when an invoice from a "new" bank account looks normal. Tocobaga's earlier look at private equity roll-ups, Same Name on the Truck, covers what buyers keep and change in the brand. The access list deserves the same scrutiny in the first 30 days:
Inventory every remote-access tool and admin account the add-on uses, and remove whatever nobody can explain.
Replace shared logins with named accounts protected by MFA.
Move email into the platform's tenant, or at minimum enforce MFA and audit mailbox forwarding rules.
Publish SPF, DKIM and DMARC for every domain the add-on sends from.
Verify by call-back every vendor bank change made in the 90 days before and after closing.
Put the add-on's IT provider on a written access agreement, or retire the relationship.
Vendor contracts deserve four questions: who on the vendor's side has admin access, whether MFA is enforced on that access, how fast access is removed when the relationship ends, and how quickly the vendor must report a breach. Stoll's intruder reached military networks by routing through a trusted lab's connection and borrowing its credibility.* A vendor's login borrows a small business's credibility the same way, and the business pays the bill when it is misused.
How do deepfake voice scams work, and how can a business spot one?
Deepfake voice scams clone a real person's voice from recordings, such as podcasts, webinars, earnings calls or voicemail greetings, and then use it to call an employee with an urgent, confidential request to move money or share credentials. A business should not try to spot the fake by ear; it should make the payment decision independent of how convincing the voice sounds, with a call-back to a known number and a second approver.
The FBI's 2025 report included its first section on artificial intelligence and tracked 22,364 AI-related complaints carrying $893,346,472 in losses.‖ Email security firm Abnormal AI, reading the same report, noted that more than $30 million of business email compromise losses were tied to AI.§§§ Those are reported losses only, and the count of firms too embarrassed to file is, by definition, missing from the total.
The most famous case is not a small business, which is exactly why it matters to one. In early 2024, a finance employee in the Hong Kong office of Arup, the British engineering firm known for the Sydney Opera House, joined a video call with what looked and sounded like the company's chief financial officer and several colleagues. All of them were deepfakes. He had been suspicious of the original email. The faces on the call talked him out of it, and he made 15 transfers totaling HK$200 million, about $25.6 million.‖‖‖ Arup's global chief information officer, Rob Greig, said afterward that "the number and sophistication of these attacks has been rising sharply in recent months."‖‖‖
Small firms are softer targets for a simple reason: the owner's voice is public and the approval chain is short. Any owner with a podcast, a YouTube channel or a recorded webinar has published training data, Law Smith included, whose voice runs through every episode of the ROI Podcast. A managing partner "calling from the airport" to rush a settlement disbursement, a CEO "stuck in a board meeting" who needs gift cards for a client, a supplier's controller "confirming" a new remittance account: the script changes, the structure does not. Urgency, secrecy and a new destination for money.
The defenses are procedural, not technical:
A spoken code phrase for any money request, agreed in person and never written in email.
A call-back to a number already on file for any request involving money, credentials or gift cards, even when the caller is on video.
Two-person approval above a set dollar threshold, with no exception for the boss.
A standing rule that urgency plus secrecy plus a new account means slow down, not speed up.
A casual question only the real person could answer.
The same generative tools that draft a passable sales email now draft a passable CFO. The response is the one Clifford Stoll used in 1986. The intruder's sessions ran on real users' accounts and looked legitimate; Stoll ignored what the accounts claimed to be and followed the phone lines instead, a channel the intruder did not control.†
What do cyber insurers require from small businesses in 2026?
Cyber insurers have become the de facto standard-setters for small business security, because their applications ask point by point whether controls such as multi-factor authentication protect email, remote access and critical systems, and carriers price, restrict or deny coverage based on the answers. An inaccurate answer on that application can void the policy after a loss.
The cautionary tale is Travelers v. International Control Services. Travelers alleged that the Illinois electronics manufacturer's application said it required MFA for email, remote network access, servers and other critical systems; after a ransomware attack in 2022, Travelers' investigation found MFA protected only the firewall.¶¶¶,**** Travelers sued on July 6, 2022, and on August 26, 2022, the court entered judgment rescinding the policy, with ICS agreeing to it.**** The company had paid premiums for coverage that, legally, never existed.
The upside of carrier scrutiny is real. Coalition reported that 64 percent of its closed claims in 2025 were resolved with no out-of-pocket loss for the policyholder, and it recovered $21.8 million in stolen funds, about $202,000 per recovery.†† Coverage is still thin where it may matter most: in the ABA's 2023 Cybersecurity TechReport, only 40 percent of lawyers reported that their firms carried cyber insurance, and just 37 percent at firms of 2 to 9 attorneys.‡‡
The practical rule is to treat the application like a sworn statement. The IT provider answers the technical questions in writing. The broker supplies the carrier's list of required and credited controls before renewal, and the gaps get closed before the form is signed, not after. Screenshots showing MFA enforcement and dated backup tests go in a folder. That folder is a logbook, and after a loss it is the difference between a claim and a lawsuit. The questions on these forms, starting with MFA, read like a good IT provider's short list, which is the quiet tell: when the people who pay claims and the people who prevent them agree on the list, the list is probably right.
How much does basic cybersecurity cost a small business per month?
For a 12-person firm, a practical cybersecurity stack runs roughly $600 to $815 a month, or about $7,200 to $9,800 a year, depending on what the firm already licenses and what its IT provider charges to patch and watch. Against a single average ransomware claim of $269,000, the math is not close.††
The worked example is a 12-person management consultancy in Tampa's Westshore district billing $2.4 million a year. The monthly stack uses published prices where they exist and stated assumptions where they do not:
Microsoft 365 Business Premium for EDR, device management and conditional access: 12 users at $22, or $264.
1Password Business: 12 users at $7.99, or $95.88.
Immutable cloud backup for servers and Microsoft 365 data: assume $150.
Three hardware security keys for the people who approve payments: assume $180 one time, or $5 a month over three years.
Extra IT provider time to patch edge devices and watch the EDR console: assume $300.
Total: $814.88 a month, or $9,778.56 a year.
Now the other side of the ledger. Verizon's 2026 report put the median ransom payment at $139,875, which buys 14.3 years of the stack.§§ Coalition's average ransomware claim of $269,000 buys 27.5 years, and its average funds transfer fraud loss of $141,000 buys 14.4 years.†† Downtime is the number nobody budgets: at $2.4 million in revenue over 250 working days, the firm bills about $9,600 a day, so ten business days offline costs $96,000 in revenue before a single recovery invoice arrives.
The breakeven is the cleanest way to see it. Dividing $9,778.56 by $269,000 gives 3.6 percent. If the checklist lowers the firm's annual odds of one average ransomware claim by 3.6 percentage points, it pays for itself on that one risk alone, before counting wire fraud, downtime, client notification or the senior consultant who quits over the stress. A firm already paying for Business Standard spends only the $8-per-user difference for Premium, $96 a month, and one using Bitwarden at $4 a user spends $48 for passwords, which drops the stack to about $599 a month.†††,‖‖
Tocobaga's earlier piece on proving marketing ROI, The Map Is Not the Pump, argued that a number nobody measures is a number nobody manages. Security spending works the same way. The firm that writes down what the stack costs and what one bad Friday would cost has already done the hard part. The rest is a purchase order.
What is the strongest case against spending more on small business cybersecurity?
The strongest case against more cybersecurity spending at a small business is that most firms never suffer a catastrophic incident, insurance absorbs much of the damage when they do, and every dollar and hour spent on security is a dollar and hour not spent on growth. That argument deserves a fair hearing, because parts of it are true.
The data gives the skeptic real ammunition. Coalition's average business email compromise loss fell 28 percent to $27,000 in 2025, a painful number but a survivable one for most firms with a few million in revenue.†† Ransom payments are falling, refusals are rising, and 64 percent of Coalition's closed claims cost the policyholder nothing out of pocket.†† The headline breach costs are skewed by large companies; IBM's 2025 average of $10.22 million for a U.S. breach, a record, describes a world most 12-person firms will never see.‡‡‡ And security theater is real: vendor sprawl, per-seat tools nobody configures, and quarterly phishing tests that teach staff to fear email instead of reporting it.
The skeptic's best line is about opportunity cost. A 12-person firm that spends $10,000 a year on security has $10,000 less for a hire, a campaign or a cash cushion. If the probability of disaster is low, the expected return on a growth dollar can beat the expected return on a security dollar. That is not reckless. That is capital allocation.
Here is where it breaks. The checklist Tocobaga recommends is not theater; most of it is configuration and habit, and the single most valuable item, the call-back rule, costs nothing. Insurance only pays if the controls on the application were real, as International Control Services learned when its policy was rescinded.**** And the "it won't happen to us" assumption has a famous test case. In June 1983, after watching WarGames at Camp David, Ronald Reagan asked the chairman of the Joint Chiefs, Gen. John Vessey, "could something like this really happen?" A week later Vessey reported back that the problem was much worse than the president thought, and about a year later the first presidential directive on computer security followed.†††† Small business owners rarely get a general's briefing. They get a 75-cent discrepancy, and a choice about whether to chase it.
So the honest verdict splits the difference. The skeptic is right about the expensive stuff and wrong about the cheap stuff. Buying more security tools is rarely the answer; doing the boring ten items well, then spending the rest on growth, usually is.
What do SPF, DKIM and DMARC have to do with marketing?
SPF, DKIM and DMARC are DNS records that tell inbox providers which servers are allowed to send email for a company's domain, and they protect marketing twice: they keep legitimate newsletters and invoices out of spam folders, and they make it much harder for criminals to send convincing email that appears to come from the company. Since February 1, 2024, Google has required every sender to Gmail to use SPF or DKIM, and bulk senders of more than 5,000 messages a day to use SPF, DKIM and DMARC, with spam complaint rates kept below 0.3 percent.‡‡‡‡
A DMARC policy of "none" satisfies Google's bulk-sender minimum and starts the reporting, but it does not stop spoofing.‡‡‡‡ The goal is to identify every legitimate sender, including the email marketing platform, the CRM, the invoicing system, the scheduling tool and the website's contact form, align them, and then move DMARC to quarantine and eventually reject. That project takes weeks, not years, and it is where marketing and security share a budget line. A domain that crooks can spoof is a domain whose real emails get filtered, and an email program built on a spoofable domain is renting its deliverability from luck.
Ownership is the other half. The domain registrar, the DNS host, the website platform, Google Ads, Meta Business, the Google Business Profile, analytics and the email platform should all be owned by the company, with at least two owner-level admins who are employees or principals, MFA on every one, and agencies granted user-level access under the company's account, never the reverse. Tocobaga's earlier piece on law firm websites, The Company Town Website, walked through what happens when the agency owns the house. In a security incident, the cost of that arrangement is not philosophical; it is the hours spent proving to a registrar that the business owns its own name while its website points somewhere it should not.
That is the slice of the problem Tocobaga works on every day. The Tampa agency audits who owns the domain, website and ad accounts, sets up SPF, DKIM and DMARC alongside email programs, and builds marketing that a security incident cannot hold hostage. Tocobaga is not an IT security firm and will say so, then point owners to a qualified provider when the problem lives in the server room. The model is plain: flat fees, never a percentage of ad spend, no auto-renewing contracts, the client owns every account and asset, and no Tocobaga name gets stamped on a client's website. It is not for everyone. For owners who want a second set of eyes on the marketing side of their risk, an intro call starts at (813) 534-1261 or hello@solvinghow.com through SolvingHow.com.
What should a small business do in the first hour after a cyberattack?
In the first hour after a cyberattack, a small business should call its bank's fraud line if money moved, isolate affected devices without wiping them, call the insurer's breach hotline before hiring anyone, and start a written log with timestamps of everything that happens. Those four moves protect the money, the evidence, the coverage and the record.
The plan has to live on paper, because the laptop with the contact list may be the one that is encrypted and the email system may be the one the attacker controls. One printed page in the office, plus a photo of it on each owner's phone, covers it:
If money moved, call the bank's fraud department first and ask for a recall, then file a report with IC3.
Disconnect infected machines from the network, but do not power them off or wipe them.
Call the cyber insurer's hotline before hiring any outside firm, so the response stays covered.
Call the IT provider and, if the insurer assigns one, the breach coach or outside counsel.
Switch to out-of-band communication, such as personal phones, in case email is compromised.
Reset passwords and revoke sessions for affected accounts from a clean device.
Write everything down with times: what was seen, who was called, what was changed.
Hold client and public statements until counsel reviews notification duties.
The urgency is measurable. The FBI's Financial Fraud Kill Chain froze 58 percent of the attempted theft it worked in 2025, and it can only work on what gets reported while the money is still moving.‖ A firm that spends the first hour debating whether the problem is real has already lost the hour that counts.
Most small firms do not have the page. In the ABA's 2023 survey, only 19 percent of lawyers at firms of 2 to 9 attorneys, and the same share of solo practitioners, reported an incident response plan.‡‡ The plan does not need to be clever. Clifford Stoll's was not. He had borrowed printers, a pile of paper and a logbook in which he wrote down every session, every trace and every call to agencies that did not care about 75 cents. Months later, he wrote, "buried clues to the intruder's origin rose to the surface" when he reread the old notes.* That logbook is what caught Markus Hess. Not a firewall, not a product, not a genius: a record kept by a man who took a small number seriously.
Every small business gets its 75 cents. It is a login from a city nobody visits, a vendor's new bank in a new state, a backup report that stopped arriving in March, a voice on the phone that sounds exactly like the boss and asks for exactly the wrong thing. The checklist exists to make sure somebody notices. Stoll put it plainly in 1988: security is "a human problem that cannot be solved by technical solutions alone."* A KGB source lost to an astronomer who would not round 75 cents down to zero. The bookkeeping caught the spy, and in 2026 the bookkeeping is still the job.
What cybersecurity does a small business need at minimum?
At minimum, a small business needs multi-factor authentication on every account, a password manager, automatic software updates and a call-back rule before any change to payment details. CISA's Secure Our World guidance names four basics: recognize and report phishing, use passwords of at least 16 characters that are random and unique, turn on MFA, and update software. The next priorities are endpoint detection and response, immutable backups that get tested, and a printed incident plan.
How can a business tell if a request to change payment details is fake?
Usually it cannot tell by looking, which is why the safest process ignores how legitimate the request appears. Any change to bank details, wiring instructions or payee accounts should be verified by calling a phone number already on file, never one supplied in the email or text. A second person should approve changes above a set amount. Red flags include urgency, secrecy, a new bank in a different state, and requests timed near a closing or month-end.
What do cyber insurers typically require before issuing a policy?
Insurers focus on a short list of controls, starting with multi-factor authentication on email, remote access and critical systems, and they ask about them directly on the application. Accuracy matters: in Travelers v. International Control Services, a policy was rescinded in 2022 after the insurer found MFA protected only the firewall. Owners should have their IT provider answer technical questions in writing and keep dated proof that each control is in place.
How can someone spot a deepfake voice or video call?
Detecting a good deepfake by ear or eye is unreliable, so the defense is procedural. Any request involving money, credentials or gift cards should be verified with a call-back to a known number, even when the caller appears on video. A spoken code phrase agreed in person adds a second check. In the Arup case in 2024, a Hong Kong employee transferred about $25.6 million after a video call in which every other participant was a deepfake.
Should a small business pay a ransomware demand?
Most victims now refuse. Verizon's 2026 data found 69 percent of ransomware victims did not pay, and Coalition reported a record 86 percent of its policyholders declined in 2025. Paying does not guarantee a working decryption key or the deletion of stolen data, and it can raise legal questions if the attackers are sanctioned. The decision should involve the insurer, outside counsel and the IT responder, and the strongest negotiating position is a tested, immutable backup.
Is Microsoft 365 secure enough for a small business out of the box?
Not by default. Microsoft 365 Business Premium includes strong tools, such as Defender for Business, Intune device management and conditional access, but they must be configured: MFA enforced for every user, legacy sign-in methods blocked, devices enrolled and alerts monitored by a named person or IT provider. Business Basic and Standard lack several of those features. Microsoft 365 data also needs its own backup, because retention settings are not the same as a restorable copy.
How often should a small business test its backups?
At least quarterly, with a real restore rather than a glance at a dashboard. A useful test restores a critical system, such as the accounting file or the ERP database, to a separate machine and records how long it took. That number becomes the firm's realistic recovery time. At least one copy should be immutable and protected by separate credentials, so attackers who steal an administrator account cannot delete the backups before launching ransomware.
Does a small business need DMARC if it only sends a few emails?
Yes, because DMARC protects the domain even when the business sends little mail. Without it, criminals can more easily send email that appears to come from the company, a common setup for invoice fraud against its customers and vendors. Google requires every Gmail sender to use SPF or DKIM, and bulk senders over 5,000 messages a day must also publish DMARC. Starting at a policy of none and moving to quarantine or reject is standard practice.
Sources
- *
- Stoll, Clifford. "Stalking the Wily Hacker." Communications of the ACM, May 1988, reproduced by the National Security Archive at George Washington University. Describes detecting the intruder at Lawrence Berkeley Laboratory in August 1986, his attacks on about 450 computers and entry into more than 30 over about ten months, printers capturing nearly every keystroke, the logbook whose "buried clues to the intruder's origin rose to the surface," dictionary cracking of about 20 percent of user passwords, and the lines that "almost nobody except LBL detected him" and that security is "a human problem that cannot be solved by technical solutions alone." https://nsarchive.gwu.edu/sites/default/files/documents/5626281/Clifford-Stoll-Communications-of-the-ACM.pdf
- †
- Snapp, Martin. "How a Berkeley Eccentric Beat the Russians, and Then Made Useless, Wondrous Objects." California Magazine, Cal Alumni Association, March 28, 2016. Stoll's 75-cent accounting error, the unauthorized user who used about nine seconds without paying, the teleprinter attached to the line, the phony SDInet folder, and the Deutsche Bundespost trace to the hacker's home in Hanover, West Germany. https://alumni.berkeley.edu/california-magazine/spring-2016-war-stories/how-berkeley-eccentric-beat-russians-and-then-made/
- ‡
- Garfinkel, Simson L. "Computer Caper Culprit Caught." The Christian Science Monitor, October 13, 1989. Reports that roughly one in 50 computers the intruder tried had an account named FIELD with the password SERVICE, that the FBI would not engage until classified information was stolen or more than half a million dollars in computer resources were lost, and that Martha Matthews, a Berkeley law student, devised the ruse. https://www.csmonitor.com/1989/1013/dbegg.html
- §
- Guinness World Records. "First Incident of Cyber-Espionage." Accessed October 26, 2026. Hess, the group's leading hacker, was arrested June 29, 1987 and convicted of espionage with two co-conspirators on February 15, 1990; the group sold information to the KGB and received 30,000 Deutschmarks. https://guinnessworldrecords.com/world-records/612868-first-incident-of-cyber-espionage
- ‖
- Federal Bureau of Investigation, Internet Crime Complaint Center. "2025 Internet Crime Report." FBI IC3, April 2026. Reports 1,008,597 complaints and $20.877 billion in losses, 24,768 business email compromise complaints with $3,046,598,558 in losses, 22,364 AI-related complaints with $893,346,472 in losses, and the Financial Fraud Kill Chain freezing $679,013,183 of $1,163,919,846 attempted (58 percent) across 3,900 incidents. https://www.ic3.gov/AnnualReport/Reports/2025_IC3Report.pdf
- ¶
- Underhill, Ken. "New Verizon Report Reveals the Security Gap Attackers Are Exploiting Most." TechRepublic, May 21, 2026. Reports 2026 DBIR findings: vulnerability exploitation as the top initial access vector at 31 percent, credential abuse at 13 percent, ransomware in 48 percent of breaches, SMBs at about 96 percent of ransomware victims of known size, third parties in 48 percent of breaches (up from 30 percent), only 26 percent of critical CISA KEV flaws fully remediated with median remediation rising from 32 to 43 days, across more than 22,000 confirmed breaches. https://www.techrepublic.com/article/news-verizon-dbir-vulnerability-exploitation-2026/
- **
- Cybersecurity and Infrastructure Security Agency. "Secure Our World: 4 Easy Ways to Stay Safe Online." CISA, September 2024. Lists recognizing and reporting phishing, passwords of at least 16 characters that are random and unique (with a password manager), turning on multifactor authentication, and updating software. https://www.cisa.gov/sites/default/files/2024-09/Secure-Our-World-4-Easy-Ways-Stay-Safe-Online-Tip-Sheet.pdf
- ††
- Coalition. "2026 Cyber Claims Report" (announcement). Coalition, March 5, 2026. Reports BEC and funds transfer fraud at 58 percent of incidents, funds transfer fraud averaging $141,000 with 52 percent originating from BEC, BEC severity down 28 percent to $27,000, ransomware as the costliest claim type at $269,000 with initial demands up 47 percent and a record 86 percent refusing to pay, $21.8 million recovered at about $202,000 per recovery, and 64 percent of closed claims resolved with no out-of-pocket loss. https://www.coalitioninc.com/announcements/2026-cyber-claims-report
- ‡‡
- Simek, John. "2023 Cybersecurity TechReport." American Bar Association Law Practice Division, 2023. Reports that 54 percent of attorneys said two-factor authentication was available at their firms, cites Microsoft data that MFA stops 99.9 percent of credential-based account attacks, and finds incident response plans at 19 percent of solo and 2-to-9-attorney firms and cyber insurance at 40 percent overall and 37 percent of 2-to-9-attorney firms. https://www.americanbar.org/groups/law_practice/resources/tech-report/2023/2023-cybersecurity-techreport/
- §§
- Rice, Kayla. "Top Takeaways from the 2026 Verizon Data Breach Investigations Report." SpyCloud, May 26, 2026. Reports that 73 percent of ransomware victims had an infostealer infection or credential leak in the prior year, half within 95 days, small organizations had a median of 7 credential leak events per year, 37 percent of organizations had an admin account with MFA disabled on an IaaS offering, and the median ransom fell to $139,875 from $150,000 with 69 percent not paying. https://spycloud.com/blog/top-takeaways-from-the-2026-verizon-data-breach-investigations-report/
- ‖‖
- Cybernews. "1Password Pricing 2026." Cybernews, September 8, 2026. Lists 1Password Business at $7.99 per user per month billed annually and Bitwarden Teams at $4.00 per user per month. https://cybernews.com/password-managers/1password-review/1password-pricing/
- ¶¶
- Honan, Brian. "Lessons for Organizations from the Verizon 2026 Data Breach Investigations Report." Help Net Security, May 25, 2026. Reports ransomware in 48 percent of breaches (up from 44 percent), third parties in 48 percent of breaches, a 60 percent rise in supply chain breaches, and only 26 percent of critical KEV vulnerabilities fully remediated, down from 38 percent. https://www.helpnetsecurity.com/2026/05/25/lessons-from-verizon-dbir-2026-findings/
- ***
- Sophos. "The State of Ransomware in the US 2025." Sophos, June 2025. Survey of U.S. organizations with 100 to 5,000 employees reporting exploited vulnerabilities as the root cause in 27 percent of attacks, phishing in 26 percent and compromised credentials in 23 percent, 43 percent using backups to recover encrypted data (down from 61 percent), and 51 percent fully recovered within a week. https://assets.sophos.com/X24WTUEQ/at/k7f88k4hqrgw9fqkknvctrp/sophos-state-of-ransomware-in-us-2025.pdf
- †††
- Dhaliwal, Sabrina. "Your M365 Bill Is Going Up in July: Here's What to Tell Your Clients and How to Come Out Ahead." Nerdio, June 29, 2026. Reports Microsoft 365 price changes effective July 1, 2026 (Business Basic $6 to $7, Business Standard $12.50 to $14, Business Premium unchanged at $22 per user per month) and that Premium includes Intune, Defender for Business, Entra ID P1 and Conditional Access. https://getnerdio.com/blog/your-m365-bill-is-going-up-in-july-heres-what-to-tell-your-clients-and-how-to-come-out-ahead/
- ‡‡‡
- Kapko, Matt. Coverage of IBM's "Cost of a Data Breach Report 2025." CyberScoop, July 30, 2025. Reports a global average breach cost of $4.44 million, a record U.S. average of $10.22 million, and an average of 241 days to identify and contain a breach, a nine-year low. https://cyberscoop.com/ibm-cost-data-breach-2025/
- §§§
- Abnormal AI. "$893M in Losses: What the 2025 IC3 Report Reveals About AI-Driven Cybercrime." Abnormal AI, April 15, 2026. Reports 22,364 AI-related complaints in the FBI's 2025 data and more than $30 million in AI-linked business email compromise losses. https://abnormal.ai/blog/ai-cybercrime-ic3-report-2025
- ‖‖‖
- CNN. "British Engineering Giant Arup Revealed as $25 Million Deepfake Scam Victim." CNN Business, May 16, 2024. Reports that a Hong Kong finance employee joined a video call with deepfaked versions of the CFO and colleagues and made 15 transfers totaling HK$200 million (about $25.6 million), and quotes Arup global CIO Rob Greig on attacks "rising sharply in recent months." https://edition.cnn.com/2024/05/16/tech/arup-deepfake-scam-loss-hong-kong-intl-hnk
- ¶¶¶
- Reed Smith. "Insurance Applications Under Scrutiny: Lessons from Travelers v. ICS." Reed Smith Client Alerts, July 2022. Reports that ICS's application said it required MFA for email, remote network access, endpoints, servers and other systems, that only its firewall used MFA, and that the claim followed a ransomware attack in May 2022. https://www.reedsmith.com/en/perspectives/2022/07/insurance-applications-under-scrutiny-lessons-from-travelers-v-ics
- ****
- Ponce, Meredith. "Travelers v. ICS Underscores Need to Respond Carefully to Cyber Insurance Application Questions." Lockton, September 15, 2022. Reports that Travelers sued on July 6, 2022, alleging ICS overstated its use of MFA, that MFA protected only the firewall, and that on August 26, 2022, the court entered judgment rescinding the policy with ICS's consent. https://global.lockton.com/us/en/news-insights/travelers-v-ics-underscores-need-to-respond-carefully-to-cyber-insurance
- ††††
- NPR. "'Dark Territory' Examines the Long History of Cyber War." NPR, 2016. Fred Kaplan tells Daniel Zwerdling that Reagan watched WarGames at Camp David in June 1983, asked Gen. John Vessey "could something like this really happen?", heard a week later that the problem was much worse than he thought, and issued the first presidential directive on computer security about a year later. https://www.npr.org/transcripts/472067214
- ‡‡‡‡
- Google. "Email Sender Guidelines." Gmail Help, accessed October 26, 2026. States that from February 1, 2024, all senders to Gmail must use SPF or DKIM, bulk senders of more than 5,000 messages a day must use SPF, DKIM and DMARC (policy may be none) with alignment and one-click unsubscribe, and spam rates must stay below 0.3 percent. https://support.google.com/mail/answer/81126?hl=en